Gadgets
Google Patches Pixel Modem Zero-Day Used in Targeted Attacks
CVE-2026-58704 is a high-severity Pixel cellular-modem privilege flaw Google says was exploited in limited, targeted attacks. The September 2026-09-05 patch closes it.
MOUNTAIN VIEW, Calif. · Maya Chen, Gadgets · Sep 16 2026
MOUNTAIN VIEW, Calif. - Google said Tuesday that a high-severity elevation-of-privilege flaw in the cellular modem on Pixel phones, tracked as CVE-2026-58704, was exploited in limited, targeted attacks before a September patch closed the bug.
The company’s Pixel Update Bulletin for September 2026, published Sept. 15, lists CVE-2026-58704 as a high-severity Modem issue and states there are indications the vulnerability may be under limited, targeted exploitation. Security patch levels of 2026-09-05 or later address the issues in that bulletin.
TechCrunch reported that the flaw sits in Pixel phones’ modem software and can be abused without any interaction from the owner, a so-called zero-click path that can escalate privileges beyond the modem sandbox.
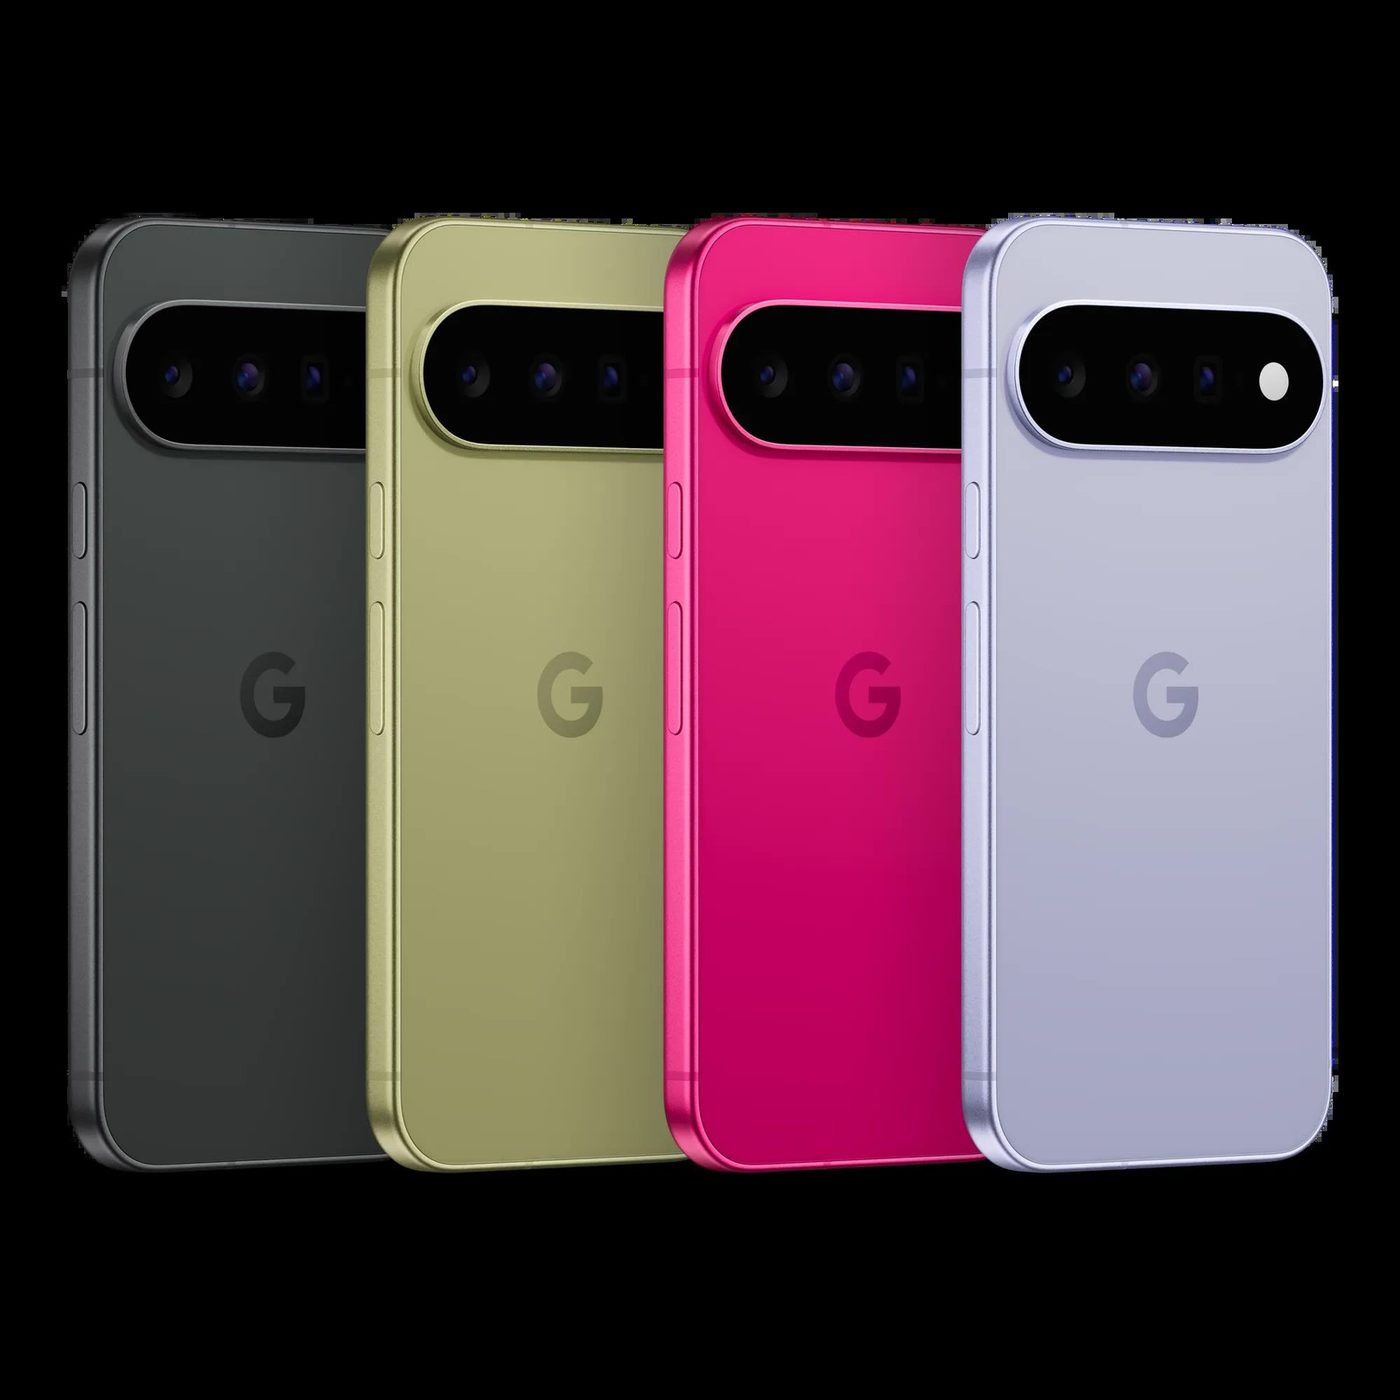 Photo: Google
BleepingComputer’s coverage of the same bulletin said the September Pixel release fixes 110 vulnerabilities affecting Google devices, including the actively exploited zero-day. The site summarized Google’s advisory language that improper authorization and protection-mechanism failures in the cellular modem can let an attacker with adjacent-network access escalate privileges in a low-complexity attack that needs no user interaction.
Google did not name who was exploiting the bug. TechCrunch noted that a Google spokesperson did not return a request for comment and that flaws of this type are sometimes abused by commercial surveillance vendors.
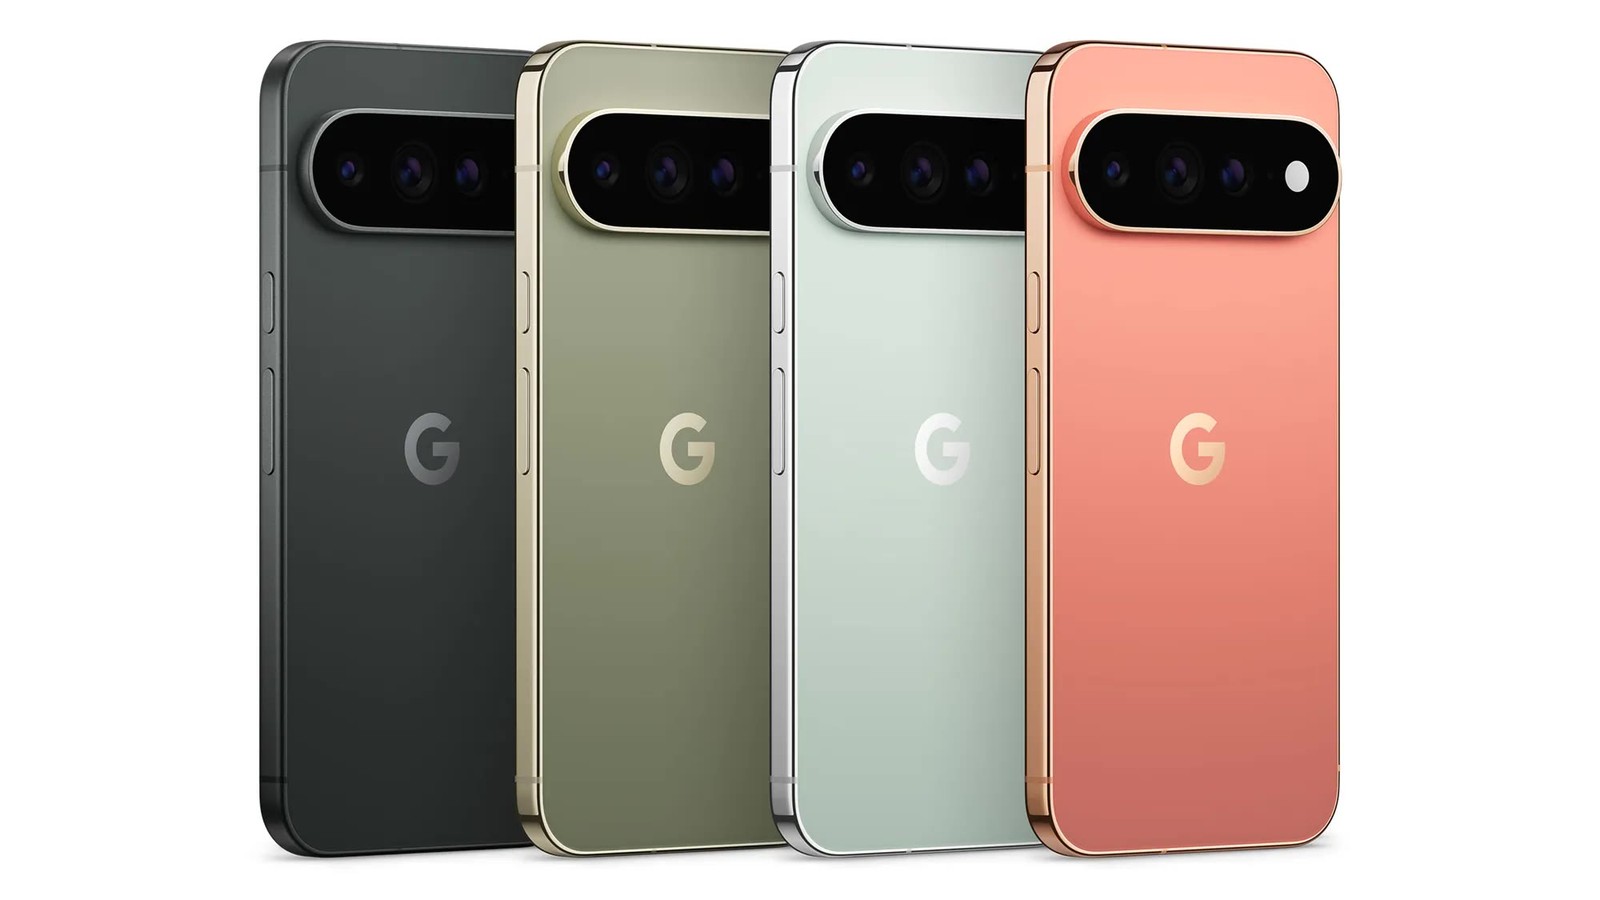 Photo: Google
Supported Pixel devices are expected to receive the 2026-09-05 patch level. Owners can install the update by opening Settings, then Security and privacy, then System and updates, then Security update, tapping Install, and restarting the phone.